ISO 42001 AIMS implementation
Across the four AIMS lifecycle phases. Senior practitioner led throughout.
STARTUP COMPLIANCE SPRINT: ISO 42001
For regulated UK organisations and AI enabled UK scaleups where AI governance is now a procurement, investor, or regulatory question. Founder led delivery. Fixed scope. No junior delegation. The certification decision rests with your certification body.
The diagnostic is free and the one-page roadmap is yours either way. The fee is confirmed in writing before work begins and does not move unless the scope changes and both sides agree in writing. A readiness service credits in full against a Sprint started within six months.
CISSP, Project Management Professional (PMP)®, ISO 27001 Lead Implementer and Lead Auditor, ISO 42001 Lead Implementer and Lead Auditor.
THE OFFER AT A GLANCE
fixed, plus VAT
Fixed. Scope confirmed on the free diagnostic.
people, single entity
One site or cloud hosted. Larger scopes are scoped on the free diagnostic.
payment options
Half at the start, half on delivery, or spread across the programme in instalments agreed on the diagnostic.
AI systems in scope
AI inventory and risk classification within the AIMS boundary.
All prices exclude VAT. Scope confirmed on the free diagnostic. Prices as published at /pricing.
Audit-ready in 8 to 12 weeks for a single entity with up to 50 people in scope and a named owner giving about four hours a week. Larger or multi-entity scopes typically take 12 to 24 weeks to audit-ready. The certification body then sets its own Stage 1 and Stage 2 dates. Read more on when it takes longer.
Phase 01
AI use across the organisation has never been formally inventoried. Risk classification is informal. Without a documented AIMS scope, every subsequent phase is built on unstable ground. Senior practitioner led scope definition and AIMS boundary work. Governance committee established. AI inventory completed with EU AI Act risk classification. Risk assessment methodology agreed at organisational level.
Phase 02
AI lifecycle management gets treated as engineering hygiene rather than a governed control. Model documentation and human oversight are inconsistent across teams. AI lifecycle controls embedded from design through decommissioning. Model documentation standards deployed across in-scope systems. Human oversight and intervention procedures formalised. AI security and robustness controls are assumed to be covered by general infosec. Bias, explainability, and accuracy testing is ad-hoc rather than systematic. AI-specific security and robustness controls deployed. Bias, explainability, and accuracy testing operationalised in the platform. Evidence collection live. Third-party AI vendor risk is invisible until something fails. AI incident response is improvised because the playbook does not exist. AI vendor and supply chain governance operationalised through the platform's third-party risk module. Incident response procedures specific to AI failure modes documented and tested.
Phase 03
Internal audit and management review are under-resourced. Evidence preparation gets rushed in the final days before certification body submission. Internal AIMS audit arranged with an auditor independent of the build. Management review structured to ISO 42001 requirements. Evidence pack audit-ready ahead of Stage 1.
Phase 04
Stage 1 corrective actions surface late. Stage 2 timing slips. AIMS handover is documented but not operationalised. Continual improvement programme established. Regulatory horizon scanning operational. Surveillance audit cadence and certificate maintenance schedule confirmed.
Across the four AIMS lifecycle phases. Senior practitioner led throughout.
Aligned to EU AI Act risk tiers and your operating context.
Model drift, bias, explainability, robustness monitored in-platform.
Reused controls surfaced and evidenced where ISO 27001 is in place.
Third-party AI risk operationalised through the platform's third-party risk module.
Tailored AI policy, supporting procedures, role-based responsibilities.
Buyer-facing AI governance signalling, configured to your brand.
Stage 1 and Stage 2 preparation with UKAS-accredited CB pathways.
The fixed fee covers a single legal entity, up to 50 people in scope, one site or cloud hosted. A larger or multi-entity scope is scoped on the free diagnostic.
Goldline builds the management system: scope and boundary, risk assessment, Statement of Applicability, the policy and procedure set written to your operating model, and the evidence structure. You name an owner who approves, attends a weekly working session and supplies what only you hold. Support runs through Stage 1 and Stage 2 with the certification body, including closing any nonconformities raised at Stage 2.
Half at the start, half on delivery, or spread across the programme in instalments agreed on the diagnostic.
Every readiness service, including the First Security Questionnaire, credits in full against a Sprint started within six months.
Certification body audit fees are billed separately and pass through at cost. Runs on your compliance platform if you have one, or in our UK-hosted GRC workspace at no extra subscription. The internal audit is carried out by an independent internal auditor appointed by Goldline, never by the team that built your system. Goldline never audits a system it implemented.
In week 1 we request quotations and Stage 1 and Stage 2 dates from three UKAS-accredited certification bodies, so you know your audit dates early. The body sets its own dates.
Built with your named owner, about four hours a week, with Goldline directing the order and reviewing every artefact.
Not sure which AI tools and systems you run? Start with the AI readiness assessment.
Article 50 transparency obligations apply from 2 August 2026 and Annex III high-risk obligations from 2 December 2027. EU buyers already require demonstrable AI governance posture before procurement signature.
UK enterprise security questionnaires increasingly include AI governance questions alongside the standard ISO 27001 and SOC 2 controls.
Buyers applying the NIST AI Risk Management Framework are accepting ISO 42001 as the equivalent international standard.
AI governance maturity is now asked at the same point in the diligence process as security and privacy posture.
Delivered by a practitioner holding both the ISO 42001 Lead Implementer and ISO 42001 Lead Auditor credentials from PECB.
Alfred Obeng holds the PECB ISO 42001 Lead Implementer and PECB ISO 42001 Lead Auditor credentials.
Senior practitioner led delivery across both standards inside one engagement. The cross-mapping work that lets ISO 27001 controls accelerate the AIMS implementation requires practitioner judgement in both frameworks.
AI-specific risk automation (model drift, bias, explainability), cross-mapped controls between ISO 27001 and ISO 42001, and buyer-facing governance information, configured on your GRC platform of choice, or ours. The platform operationalises the evidence the senior practitioner designs.
No subcontracted hours. No offshored work. No associate handoff. The practitioner who scopes the engagement is the practitioner who delivers it, from diagnostic call to certification audit.
Goldline delivers on your GRC platform of choice, or ours. Platform selection is confirmed at scoping. Goldline remains the senior practitioner delivery layer throughout.
| Deadline | What applies |
|---|---|
| February 2025 | Prohibited AI practices and AI literacy |
| 2 August 2025 | General-purpose AI models and governance framework |
| 2 August 2026 | Article 50 transparency obligations, except Article 50(2) |
| 2 December 2026 | Article 50(2) for legacy systems and new prohibited practices |
| 2 August 2027 | National AI regulatory sandboxes established |
| 2 December 2027 | High-risk obligations for Annex III standalone systems |
| 2 August 2028 | High-risk obligations for Annex I embedded systems |
If you have taken ISO 42001 Sprint without an existing ISMS, ISO 27001 is typically the next logical layer. The AIMS controls you implemented substantially reuse into a full information security management system.
Three packages on a 12-month term, billed monthly, keep the controls running and the evidence current, with independent verification.
PCI DSS, ISO 27017 and ISO 27018 (cloud), ISO 27701 (privacy), DCC for defence supply chain. Discuss in discovery.
Under Microsoft's Supplier Data Protection Requirements, suppliers delivering AI systems must provide independent assurance against Section K of the DPR, either by completing an independent assessment against Section K or by submitting ISO 42001 certification. Section K covers intended use disclosure, prohibited practices, responsible AI risk assessment, and an AI System incident response plan with rollback and feature disablement timings.
Microsoft Supplier Data Protection Requirements v12, March 2026, and the SSPA Program Guide v12Microsoft is currently the only major enterprise publishing this requirement. Others have certified their own AI services without extending the requirement to suppliers.
ISO 42001 UK Consultant: what to look for and why the credential matters£7,000 fixed
The information security management system, built by Goldline with your named owner.
View ISO 27001 Sprint£12,500 fixed
One management system for ISO 27001 with ISO 42001.
View Integrated SprintFrom £2,500
Establish the position before you commit to implementation. Credits in full against a Sprint started within six months.
View AI Governance Readiness AssessmentAll plus VAT. Half at the start, half on delivery, or spread across the programme in instalments agreed on the diagnostic. Every readiness service, including the First Security Questionnaire, credits in full against a Sprint started within six months.
Your product or operations embed AI in customer-facing or decisioning workflows: generation, classification, recommendation, or model-served processing. The AIMS scopes around these systems. Suited to regulated organisations, financial services, healthcare, defence supply chain, and AI enabled scaleups. Not calibrated for pre-revenue startups.
ISO 27001, SOC 2, or equivalent in place or in active implementation accelerates the engagement materially. Control reuse and existing evidence reduce the AIMS scaffolding required.
Designated AI governance contact, executive sponsor, and resourced engineering, data science, and security collaboration. AIMS depends on cross-functional accountability.
Modern engineering stack compatible with leading GRC platform integrations, or willingness to onboard. Platform selection is confirmed at scoping.
Documented AI use cases, preliminary view on EU AI Act risk classification, identified AI-specific risks across bias, robustness, data quality, and explainability.
If the Sprint is not the right fit, we will tell you at scoping and recommend the alternative.
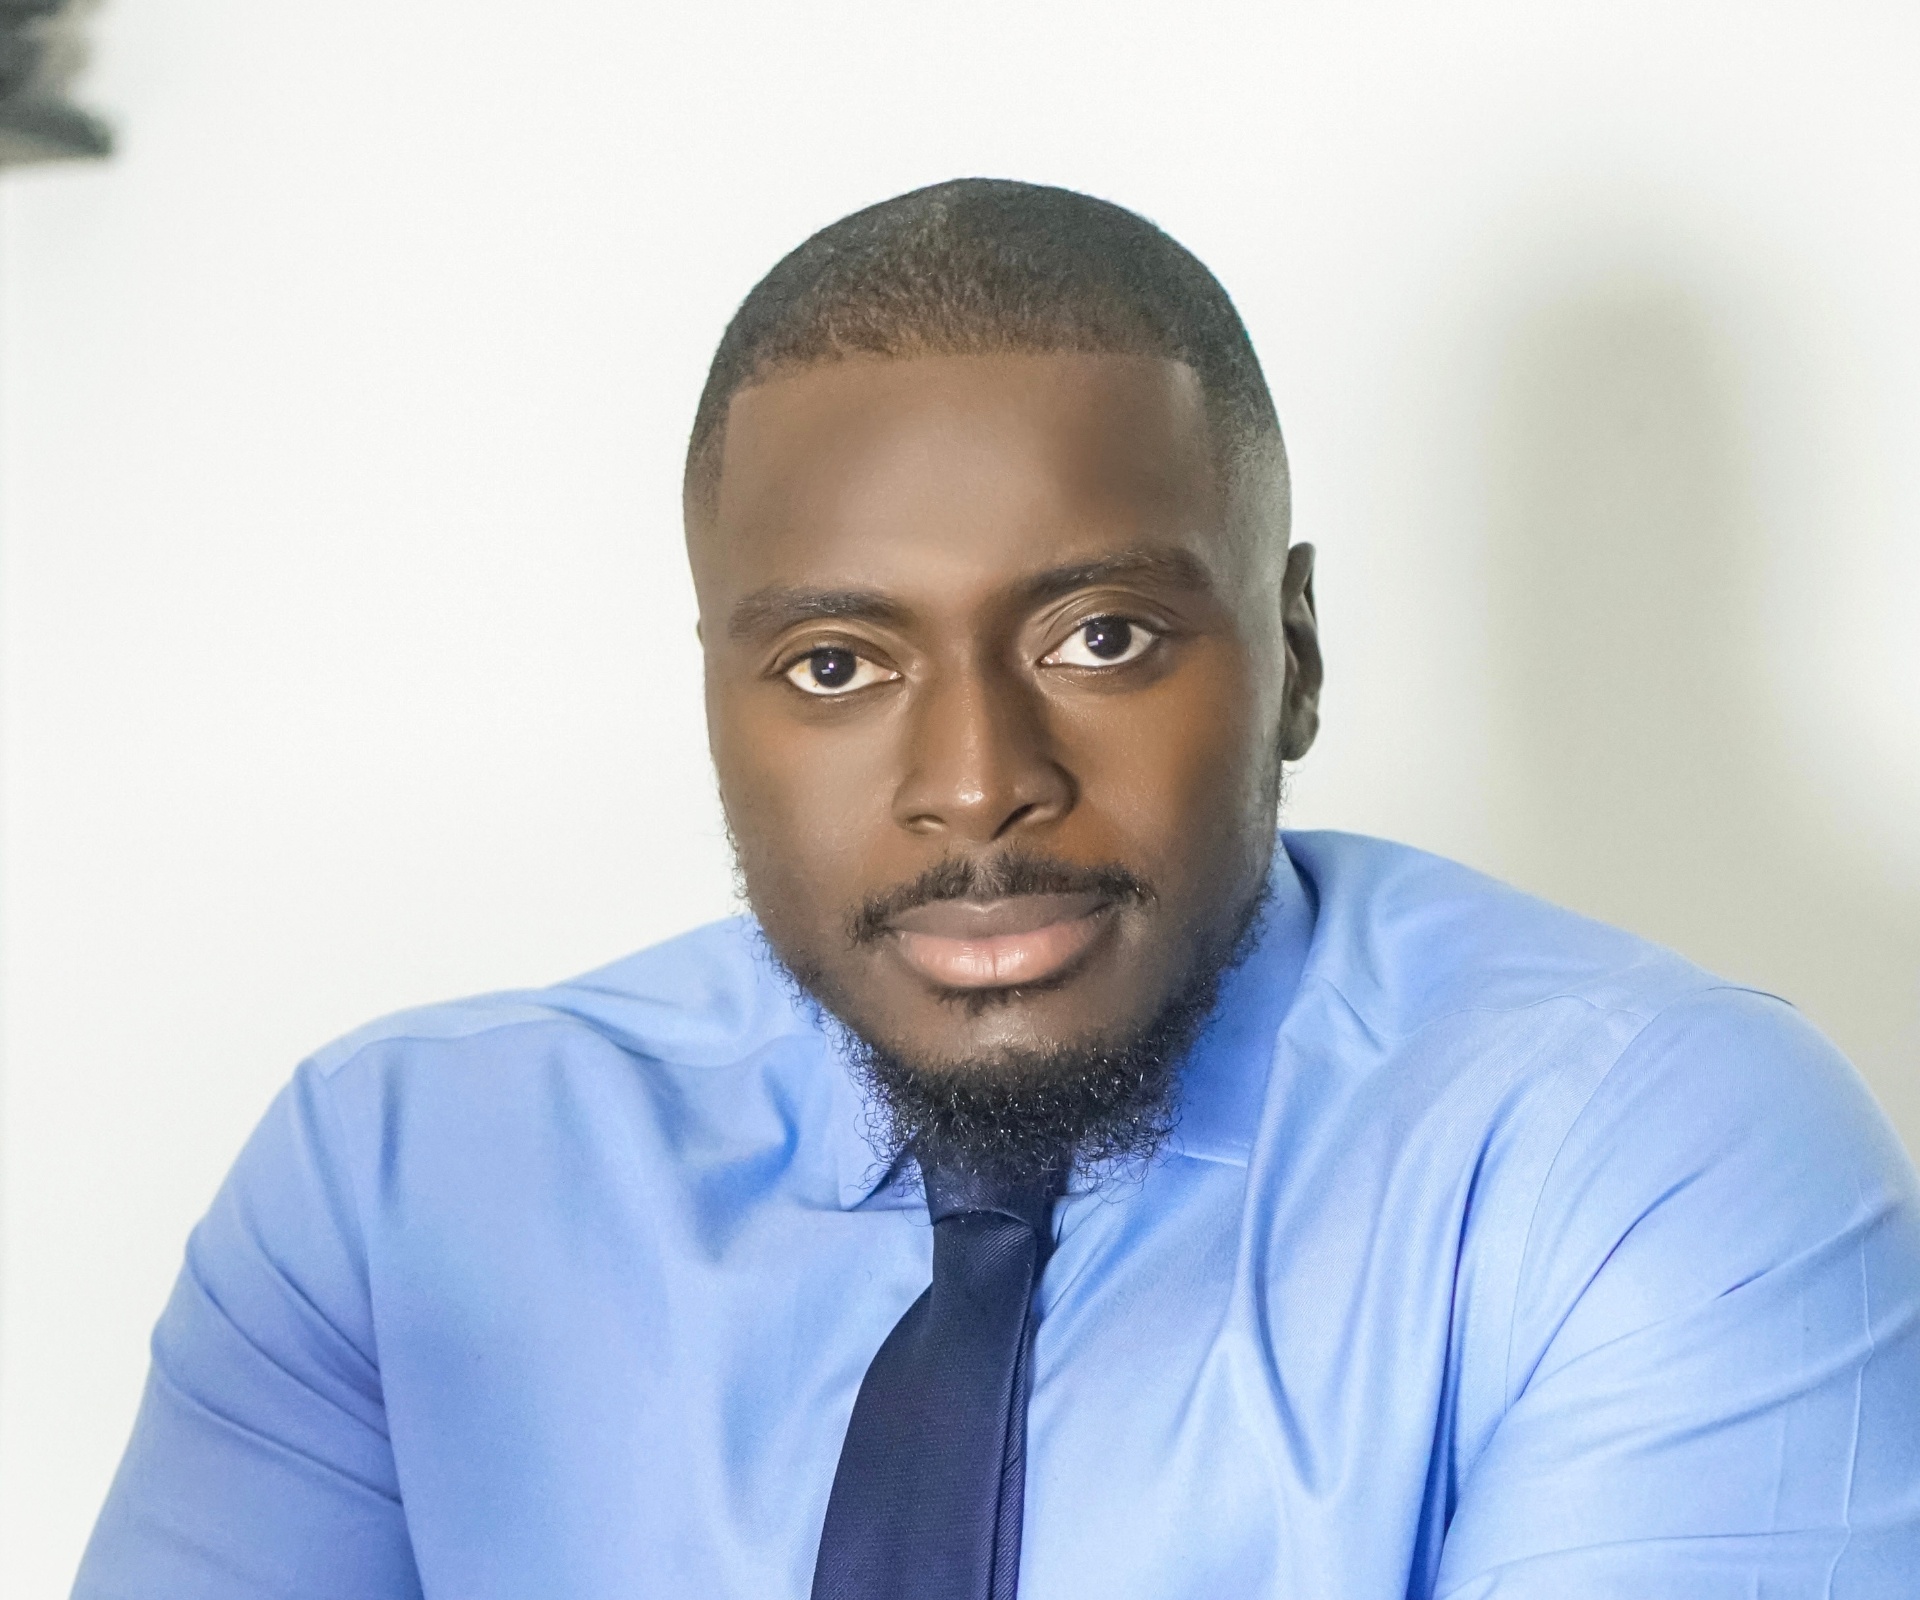
THE PRACTITIONER
CISSP, Project Management Professional (PMP)®, ISO 27001 Senior Lead Implementer and Lead Auditor, ISO 42001 Lead Implementer and Lead Auditor.
Founder and senior practitioner. ISO 42001 Sprint engagements are delivered by the practitioner who scopes them, from the diagnostic call through to the certification audit. Currently completing an Executive MBA with AI specialism at the University of Hertfordshire (December 2026).
The person who scopes it is the person who delivers it. Goldline is not a certification body. Goldline never audits a system it implemented and never sells implementation and certification to the same organisation for the same scope.
Discuss your scope. No sales pitch. No commitment. Or email Alfred directly: alfred@goldlineconsultancy.co.uk.
We use cookies to measure the site and improve it.
We use cookies and similar technologies to measure how this site is used and to measure our advertising. Until you choose, Google tags run in a consent-limited mode that sets no cookies. If you accept, we load Google Analytics 4 and Google Ads with cookies, PostHog, Plausible and Microsoft Clarity, which records session replays. Read our Cookies policy.