Your compliance platform administered by Goldline: the test queue reviewed each month and every failing test given an owner and a date rather than left to drift. You keep the integrations connected.
FOR CERTIFIED COMPANIES UNDER 50 PEOPLE
Certified.Now keep it that way.Without hiring for it.
A managed retainer that keeps your ISO 27001 or ISO 42001 certificate current: the platform, the evidence, the independent internal audit and the surveillance visit, run on a calendar rather than rebuilt before the auditor arrives.
- Independent internal audit before every surveillance visit, arranged inside the retainer
- From £1,450 a month, 12 months, plus VAT
5-star client reviewsRead them on G2
GRC platformPartnerBook the free 45 minute scoping callBring your certificate, your surveillance date and your last audit report. You leave with the retainer scope and price either way.Same-week availability
No sales pitch 45 minutes Senior practitioner
CISSP, ISO 27001 Lead Implementer and Lead Auditor, ISO 42001 Lead Implementer and Lead Auditor, PMP.
THE OFFER AT A GLANCE
£1,450
a month, one standard
£1,950 a month for ISO 27001 and ISO 42001 together. 12 month minimum. Plus VAT.
12
hours reserved a month
16 on the integrated retainer. Unused hours do not roll over.
1
independent internal audit a year
Arranged before surveillance, by an auditor who did not build or operate the system.
3
questionnaires a quarter
Five on the integrated retainer, answered from the evidence base the retainer maintains.
Prices excluding VAT. Scoping confirms the fit before anything is payable. Prices as published at /pricing.
On your own vs With the retainer
On your own
- Maintenance competes with the product roadmap and loses.
- Evidence is rebuilt in the month before the audit.
- The internal audit is run by whoever built the controls.
- Platform tests drift red and nobody owns the queue.
- The surveillance visit becomes a fire drill.
With the retainer
- A senior practitioner owns the calendar.
- Evidence stays current month by month, inside your compliance platform.
- The internal audit comes from an auditor who did not build or operate the system.
- Every failing platform test gets an owner and a date.
- Surveillance preparation starts on a date, not on a deadline.
What you get
Platform
Manual evidence for anything the platform cannot see, scheduled by you and checked by Goldline, so the platform describes the estate as it actually is.
Works inside whichever compliance platform you use, or without one; without a platform more of the reserved hours go to evidence collection.
Audit and the certification body
The independent internal audit before every surveillance visit, arranged with an auditor who did not build or operate the system; findings tracked to closure with the root cause recorded.
Certification body co-ordination: the surveillance date, every document request handled before the auditor arrives, attendance on the day and written responses to findings.
Support closing any nonconformities raised at surveillance, and recertification in year three prepared as an initial certification.
The next year planned in the final quarter: surveillance date, platform renewal, the next internal audit.
Keeping it alive through the year
A quarterly review with your named owner: the risk register against what changed in the business, the policy set against what the team actually does, the access review and the supplier review checked and evidenced.
The management review pack reviewed before each meeting, Goldline attending once a year.
One incident response exercise a year, run by Goldline and recorded by you, and one security awareness session a year with new starters covered through your platform's training module.
Customer security questionnaires reviewed before they go back, three a quarter on one standard and five on the integrated retainer.
A written view on any change that touches the scope, a 30-minute monthly call, and email access with a two working day response.
Platform licences are quoted separately and set out in full in your engagement letter. The integrated retainer also includes AI estate change tracking. Questionnaires beyond the allowance are quoted on request.
How the year runs
Auditors can tell the difference between a system that ran all year and one that ran in the month before the visit.
Every quarter
Review and monitor
Risk register review, policy review, nonconformity and corrective action review, control monitoring.
Twice a year
Supplier and access reviews
Supplier review, access review.
Every year
Prepare and evidence
Management review pack, incident exercise, awareness session, surveillance preparation, the independent internal audit.
Year three
Recertification preparation
Recertification preparation, run as an initial certification.
What it is, and what it is not
Independence
The internal audit is formed by someone who did not build or operate the system. Where Goldline operates your platform under the retainer, the internal audit is arranged with an independent auditor, and its findings land in your nonconformity register.
Your time
About two hours a week from your named owner, for reviews and approvals. You draft policies and records; Goldline reviews, checks and audits.
The certification body
An accredited body conducts surveillance and recertification and decides the outcome. Its fees are paid by you direct and pass through at cost.
Add-ons
Vulnerability scanning
Monthly external and quarterly internal, by a named provider and passed through at cost, findings entered in your nonconformity register with an owner and a date. Where Goldline itself ran the scanning, the internal audit would come from someone else.
priced at the diagnostic and fixed once agreed
Annual penetration test
A CREST test and retest by a specialist tester, not Goldline, passed through at their fee and disclosed.
priced at the diagnostic and fixed once agreed
AI system security testing
From £4,500 fixed.
priced at the diagnostic and fixed once agreed
Choose your route
Managed Compliance Retainer
£1,450 a month
One standard
View Managed Compliance RetainerIntegrated retainer
£1,950 a month
ISO 27001 and ISO 42001
View Integrated retainerNot certified yet
ISO 27001 Sprint £7,000 fixed
The information security management system, built by Goldline with your named owner.
View Not certified yetAll plus VAT, 12 month minimum, invoiced monthly, scope calibrated to your certification portfolio and questionnaire volume.
Is this you?
Certified, with no dedicated compliance function to keep the system current
Under 50 people, one legal entity
Enterprise security questionnaires arrive often enough to be a real internal cost
A surveillance date in the next twelve months
This is not for organisations with an established internal compliance team. The retainer would duplicate capability you already pay for, and targeted support such as internal audit is the better fit.
THE PRACTITIONER
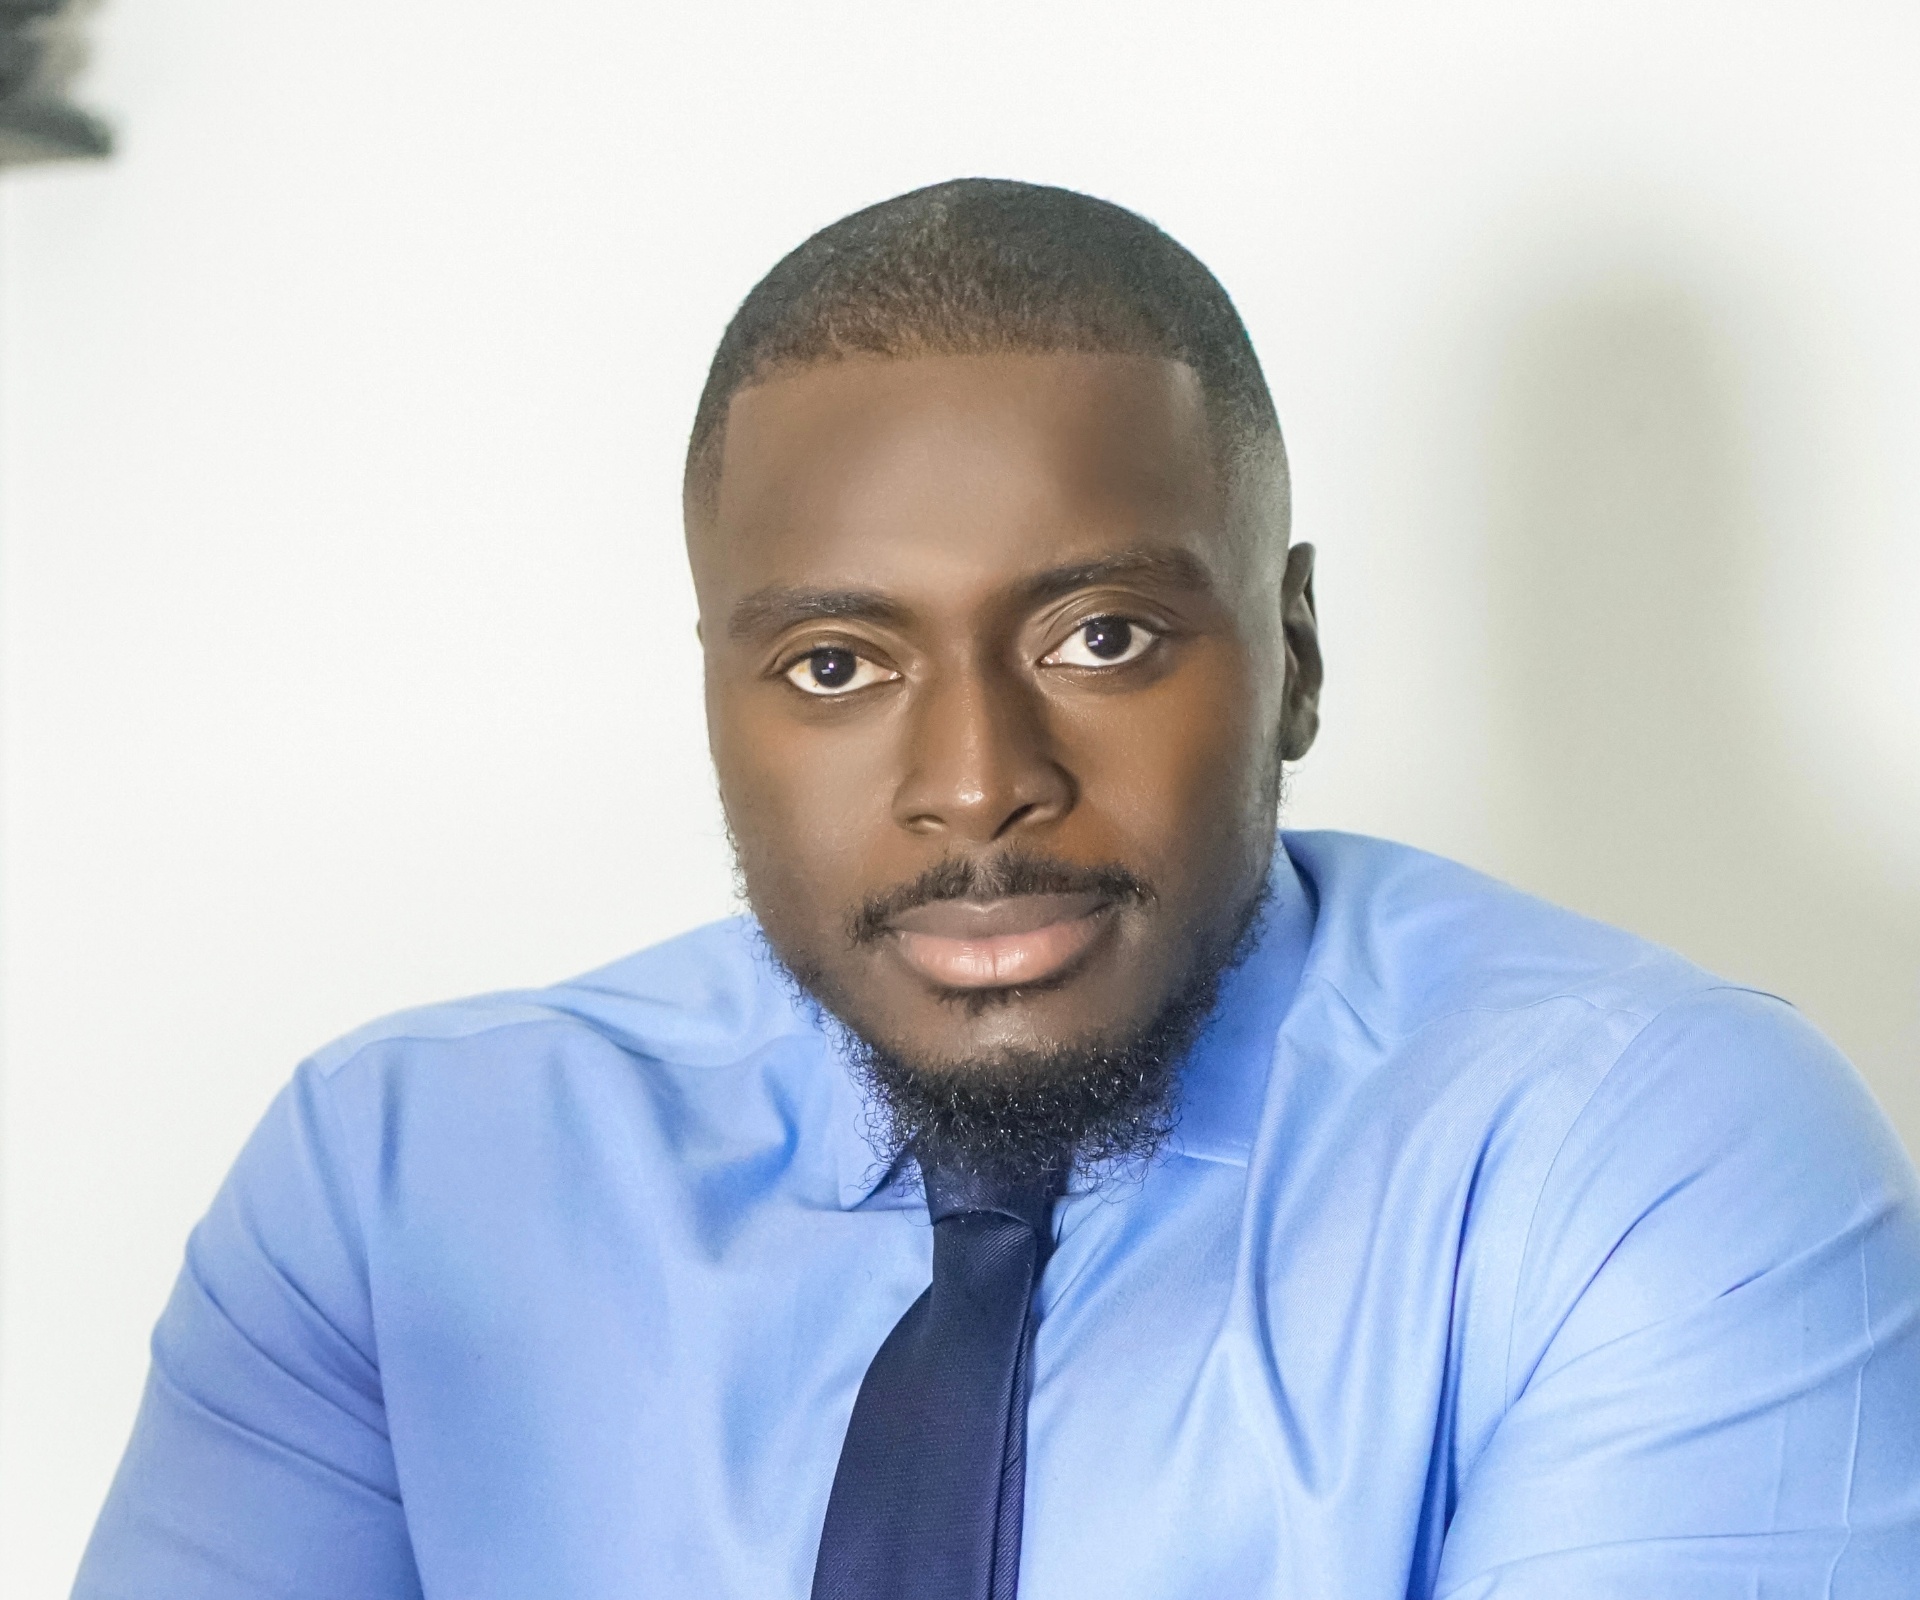
Alfred Obeng
CISSP, PMP, ISO 27001 Senior Lead Implementer and Lead Auditor, ISO 42001 Lead Implementer and Lead Auditor
The person who scopes it is the person who delivers it. Goldline is not a certification body. Goldline never audits a system it implemented and never sells implementation and certification to the same organisation for the same scope.
Common questions
Certified, and no one owns it?
A 45 minute scoping call establishes your certification portfolio, your questionnaire volume, and the right retainer scope and price. No sales pitch. If an internal hire is the better answer, we will tell you.